Delinea Secret Server Integration
This page is for Device42 administrators who use Delinea Secret Server as their secret manager and want Device42 to retrieve discovery credentials from Delinea instead of storing them locally. By the end, Device42 will securely look up and use Delinea-managed credentials for your discovery jobs.
Each Device42 discovery job is configured to use one or more sets of system credentials. If you already use Delinea Secret Server to manage passwords and other secrets, the Device42 Delinea Secret Server integration allows Device42 to securely retrieve these credentials from Delinea Secret Server as your primary secret management solution.
Delinea Secret Server offers useful features such as automatic password rotation, which can be configured to rotate secrets per your specific corporate policies and industry guidelines.
This page covers how to configure Delinea Secret Server, connect it to Device42, and use it as the credential source for discovery jobs.
Passwords retrieved from Delinea Secret Server are not viewable in Device42.
Prerequisites
Before configuring the integration, make sure you have:
- Administrator access to both Delinea Secret Server and Device42
- Network connectivity between the Device42 appliance and Delinea Secret Server
- A user account in Delinea Secret Server with the View Secret permission, plus view access to the folders you want Secrets retrieved from
While you can use any user account, it is strongly recommended that you use a dedicated application account for Device42. Application accounts are restricted from logging into the UI and can only be used via the API.
Configure Delinea Secret Server
Set up a user account and folder permissions in Delinea Secret Server before connecting to Device42.
Configure Device42
-
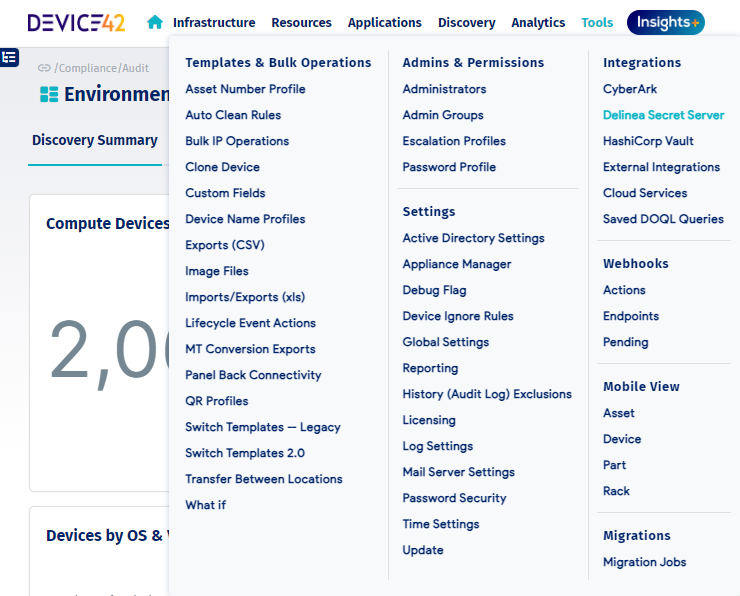
Select Tools > Integrations > Delinea Secret Server from the Device42 menu.
-
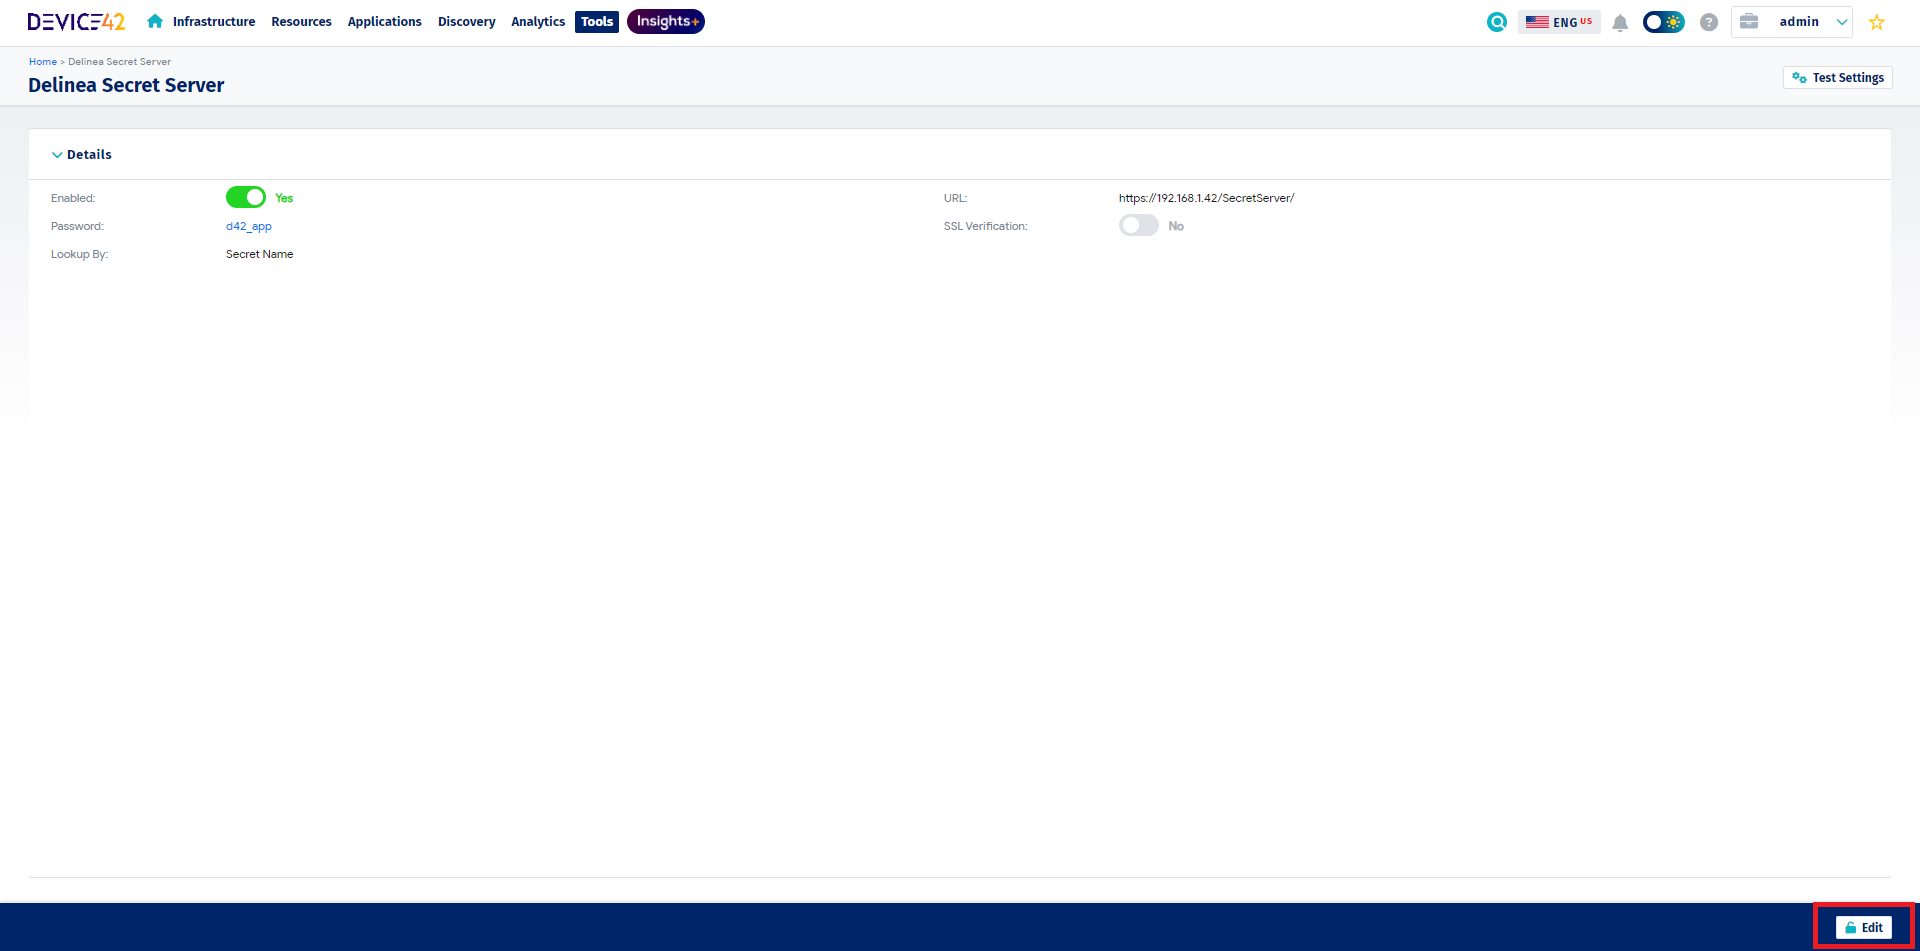
Click the Edit button in the bottom right corner and enter your Delinea Secret Server RESTful API information.
-
Verify connectivity by clicking the Test Settings button in the top right corner.
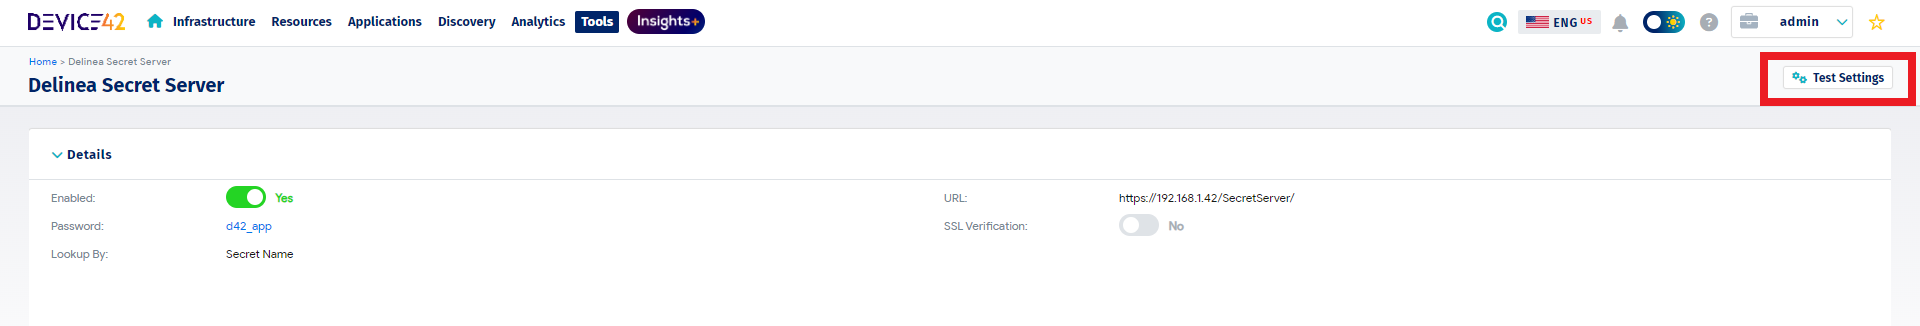
The Test Settings button validates the supplied configuration settings by retrieving a token from Delinea Secret Server. If successful, a "Delinea Secret Server Settings Valid" message appears in the top right corner.

-
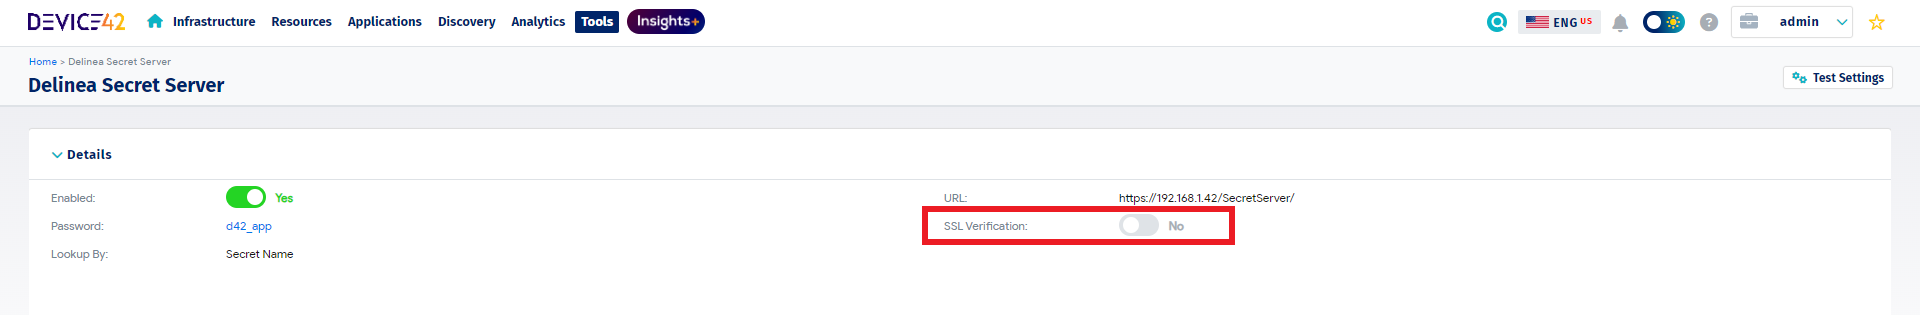
If you encounter SSL errors, disable SSL Verification on the Delinea Secret Server configuration page before trying again.
Use the Integration for Discovery
To create a new password object using Delinea Secret Server, select Delinea Secret Server from the Password Storage dropdown menu.
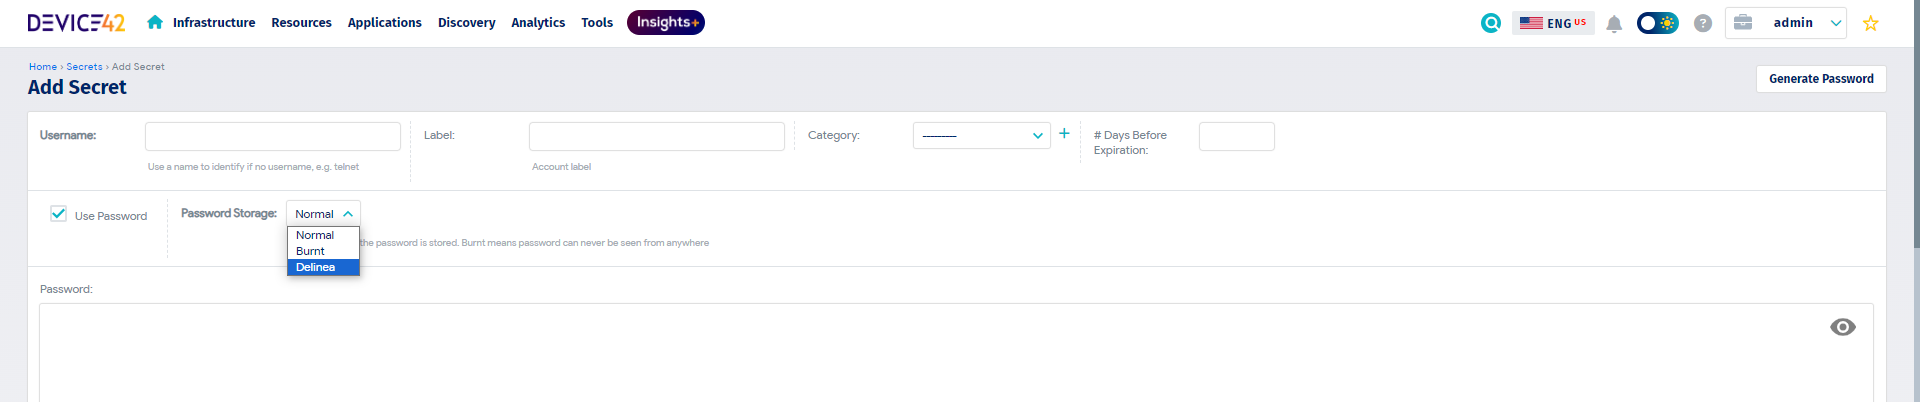
Note: By default, both usernames and passwords are retrieved from Delinea Secret Server by looking up the secret using either Secret Name or Secret ID, depending on which was selected in the configuration. The value used for the lookup is assumed to be stored in the Label field of the related secret in Device42. If there is no value for Label, the value is taken from the Username field instead.
Usernames and passwords are parsed from the secret returned by Delinea Secret Server using the slugs username and password respectively. You can override the default slugs using Password Custom Fields named username_slug and password_slug.